- Michael Patterson of Coder argued that error messages, tickets, CI logs and documentation can carry malicious instructions that coding agents accept as true.
- He said the damage grows because agents often hold broad access, and he urged running them in isolated environments with tight permissions and logging.
Michael Patterson, a staff solutions engineer at Coder, argued that the text coding agents read can be an attack channel. Error messages, support tickets, build logs and documentation all count. An agent tends to believe what it reads, and it often holds wide access. He made the case in a talk on the AI Engineer show.
What was said
Patterson used Simon Willison's term, the "lethal trifecta", for an agent that can reach private files, take in outside content and contact the internet. He said agents running on a laptop hit all three. In a secure enterprise, he argued, even two of the three is unacceptable.
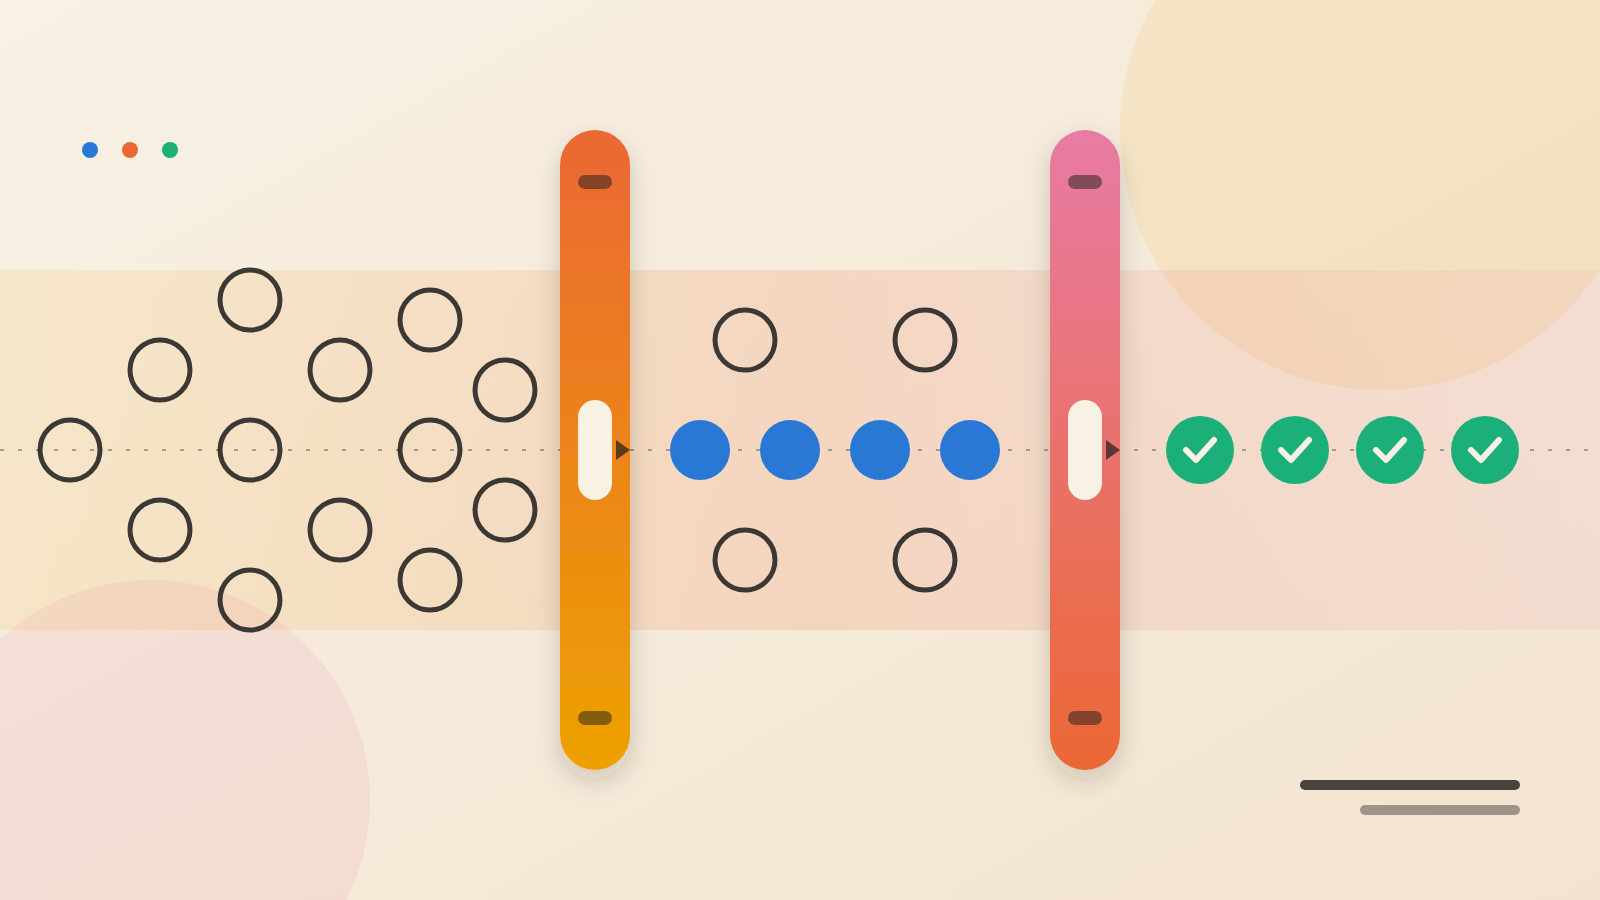
He described prompt injection as hostile instructions hidden in something the agent trusts. His examples were error messages, support tickets and CI/CD logs, the automated records of software builds and tests. Anyone who can write into those places can try it. In his words, "the agent just accepts that as a source of truth and can do something that you didn't expect it to do."
He named two related risks. Context poisoning means planting false information in documentation or data the agent will consult. Privilege escalation follows because agents are usually given reach over nearly everything, so they can finish their tasks. A successful injection could then delete a table, upload files or post content. Patterson said "usually, agentic AI can do a lot of damage really fast."
His fixes were architectural. Run the agent in an isolated cloud environment, not on a laptop. Let it reach only approved domains, with narrowly limited credentials. Route its model traffic through a proxy that logs everything and can filter out injected text. Add a firewall that blocks commands nobody approved.
Why it matters
Our reading: a ticket or log line is written for a person, who can shrug off a strange instruction. An agent that reads it with broad permissions changes the risk. That puts a question to anyone who builds or buys these tools. Who can write into the places the agent reads, and what can the agent reach once it believes them?
Patterson's list is ordinary: support queues, build output, documentation. Each one is a place where outsiders or careless colleagues may add text. If an agent reads it, that text deserves the same scrutiny as any other input.
The other side
Patterson works for Coder, which sells cloud development environments. The main remedy he recommended is close to what his company offers. He also said there was no time for a demo. The excerpts we reviewed include no tested case.
He said an incident is a matter of when, not if, but the excerpts give no incident data. He said the proxy can filter out injections, but the excerpts do not say how reliably. He also pointed to the tension at the core: agents are handed wide access because the work seems to require it. The excerpts do not say how far to narrow that access before the agent stops being worth running.
Written by the WebPulse Newsroom with AI assistance, and checked by our editorial review: every quotation was verified against the recording's transcript. How we use AI.
The conversation this talking point comes from
- AI Engineer: The Lethal Trifecta Is Already on Your Laptops — Michael Patterson, Coder (2026-10-10)