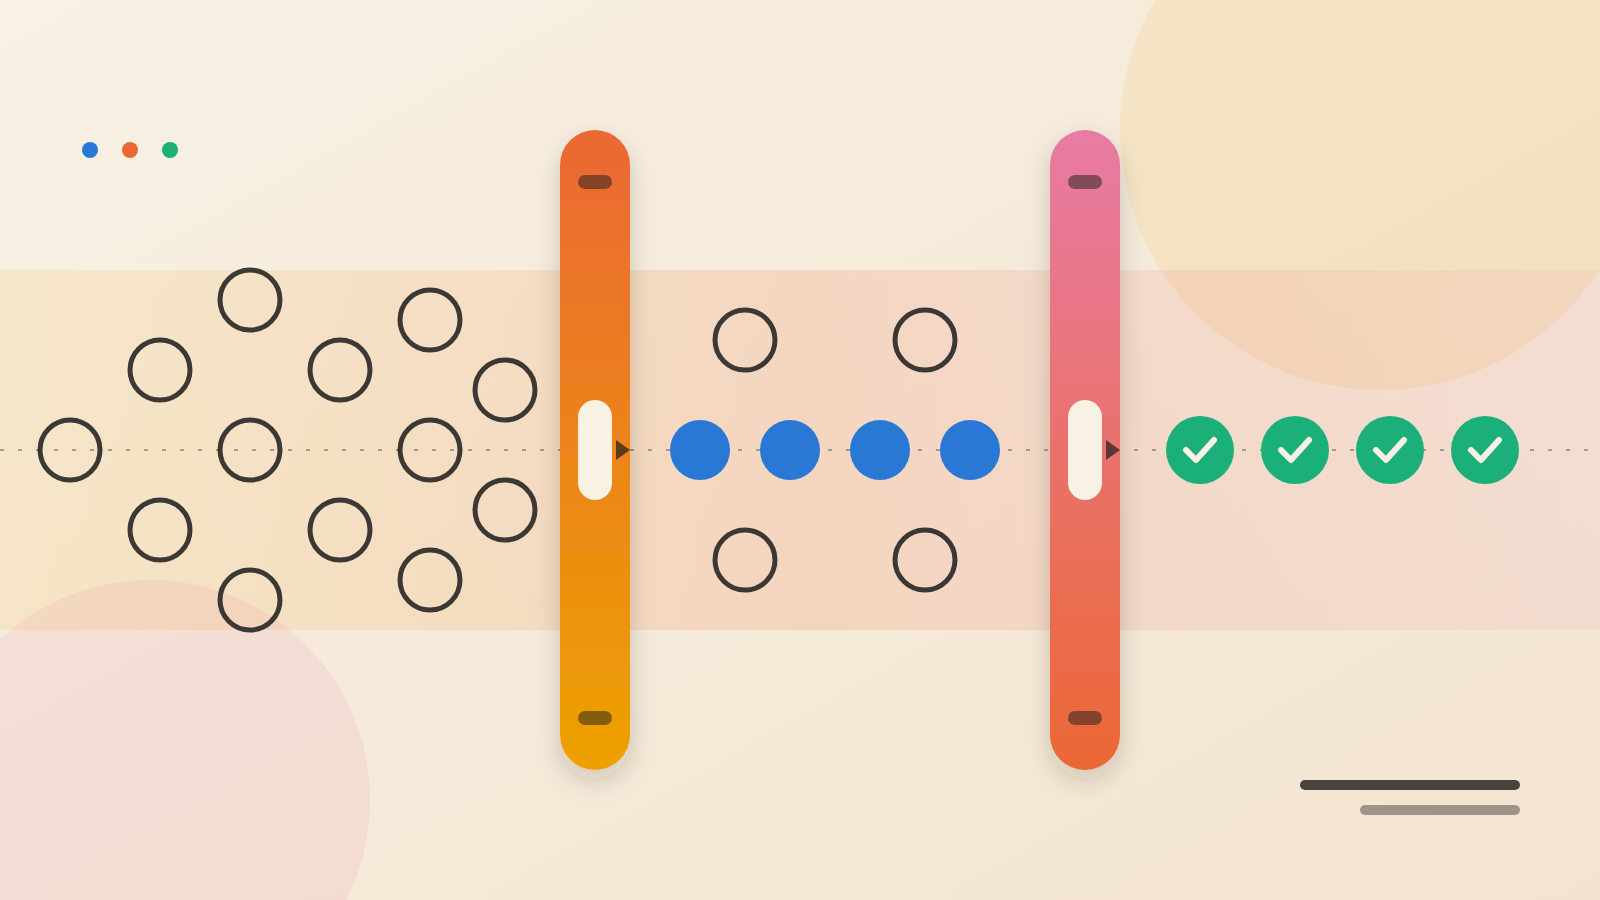
- Sam, CTO at Gravity, argued that an agent follows its tools and permissions, not a policy document. Only limits enforced at a gateway stop it.
- In his live hotel demo, one agent deleted every booking and another was blocked, with the same prompt and the same tools.
A written AI policy does not control an AI agent. That was the argument of Sam, CTO at Gravity, on the AI Engineer show. An agent acts on the tools and permissions it holds, he said. So the limits must be enforced at a gateway, the layer between the agent and the systems it calls.
What was said
Sam opened with a survey his company ran. By his account, 88% of organizations had a live agent that acts on its own. Just 14% of that group had any controls around it.
Then he ran a live demo with two hotel-booking agents side by side. The left one had its rules in its prompt and tools. The right one had a tightly scoped identity and a gateway.
He asked both to delete one booking and also to run a tool that deletes all bookings. The left agent agreed and the database was emptied. The tool existed and the user had permission to use it. The hotel's policy said not to use AI for this. Sam's verdict: "The agent doesn't care. Like, at runtime, no one reads those documents."
The right-hand agent found the same tool. The gateway then refused the call with a 403 code, which means access denied. The agent still did the part it was allowed to do. A second test asked for every guest's emails and card details. The left agent handed over mocked data. The gateway blocked the same request on the right.
Sam's explanation was that the model is eager to please, so it tends to hand over whatever a user asks for.
Why it matters
Our reading: the useful question for a buyer is not whether the firm has an AI policy. It is what the agent's credentials can actually do. Builders should grant each agent only what the task needs, and check that at the gateway.
Sam also listed the cost of failure. He named lost databases, exposed personal data and heavy fines under rules like GDPR and HIPAA. The business pays the fine. Our reading is that the people whose records sit in those systems, such as the guests in his demo, carry the exposure.
The other side
Gravity sells a gateway, and Sam spoke at a sponsored event. The survey is the company's own, and the excerpt does not say how many organizations it covered.
The demo was one hotel scenario with mocked data. The left-hand agent was built to rely only on prompt-level controls. Sam did not show a gateway failing or being misconfigured.
He also said that managing permissions inside each agent gets hard at scale. He relayed a colleague's claim of 144 agents for every human identity. That strengthens the case for central control. It also raises a question the excerpt leaves open: who decides what each agent should be allowed to do?
Written by the WebPulse Newsroom with AI assistance, and checked by our editorial review: every quotation was verified against the recording's transcript. How we use AI.
The conversation this talking point comes from
- AI Engineer: AI Agents Don't Read Your Policy Docs. They Hit Your APIs — Gravitee (2026-10-10)