- ESET's survey of 4,400 small and mid-size business leaders worldwide found two in five have no formal rules on how staff and systems use AI, even as some firms start running AI agents.
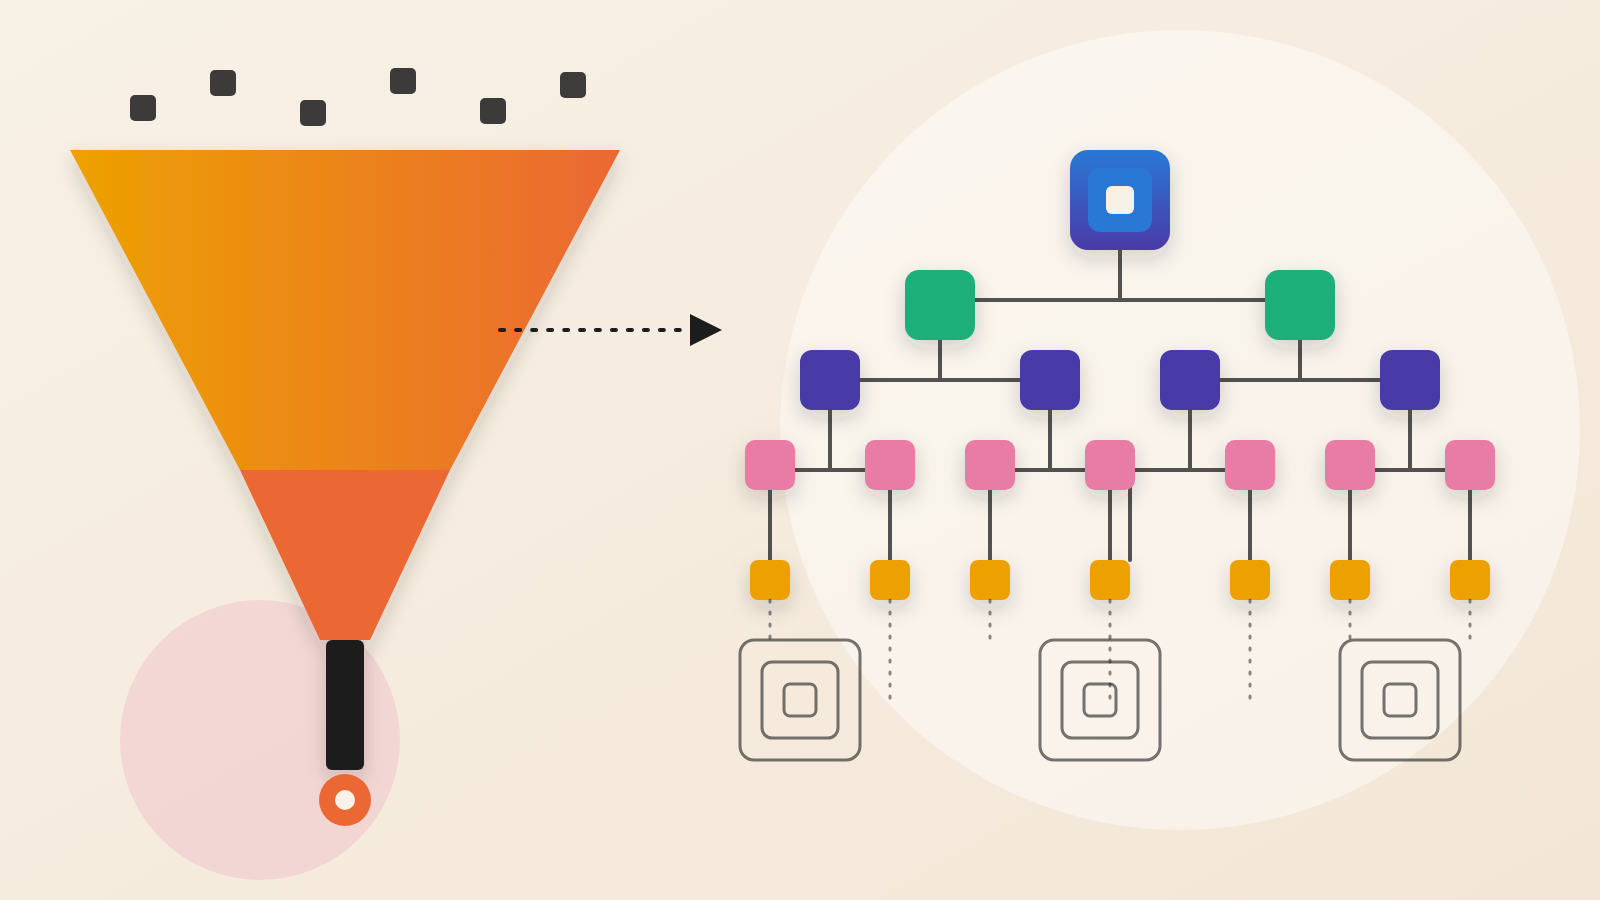
- ESET scanned nearly 900,000 AI agent skills between March and May 2026, flagged over 25,000 as suspicious, and confirmed more than 3,000 as malicious, so a check at install time is not enough.
- ESET advises business leaders to ask which agents and skills connect to company systems, who approved them, and whether any one agent combines sensitive data, outside content, and outbound messaging.
Governance is lagging adoption
Small and mid-size businesses have moved past AI chatbots and started handing work to AI agents, with some running multi-agent 'assembly lines' where a supervisor agent manages a swarm of specialist agents, according to ESET. ESET's survey spanned 4,400 SMB decision-makers worldwide; two in five reported that no formal rules yet govern how staff and systems may use AI — a measure of overall AI governance broadly, not a count limited to firms confirmed to be running agents specifically. ESET's researchers note that formal AI rules were more common at companies that had already suffered an incident — governance arriving after a breach rather than before one.
A skills marketplace with no gatekeeping
Skills are the mechanism by which an agent gains reach beyond conversation: bundled sets of instructions that tell it which actions to perform and which external tools to call. Between March and May 2026, ESET scanned close to 900,000 unique skills pulled from popular repositories. Of that pool, its scan flagged upward of 25,000 as suspicious and confirmed more than 3,000 as malicious, capable of harvesting credentials, exfiltrating data, or executing remote code. ESET points out that a one-time check at install time isn't sufficient, since a skill's upstream instructions or services can change afterward — the 'rug pull' scenario where a tool that behaved normally later turns into an infostealer.
Familiar attacks, faster execution
AI-specific risks haven't displaced the established paths into company systems. In its SMB Cyber Readiness Index 2026, ESET ranks phishing and the exploitation of known software flaws as the breach causes it sees most often. Citing Microsoft's figures, ESET notes that phishing emails generated with AI convert at a 54% click-through rate, more than four times the 12% rate for conventional phishing attempts. ESET attributes part of that gap to cost: generating convincing, individualized lures at scale has become inexpensive with AI, letting attackers construct messages that slip past the checks employees have been trained to run. Separately, ESET's tally of roughly 500 known exploited vulnerabilities logged in the first half of 2026 shows close to a quarter were already under active attack by the day each one was disclosed — a lag defenders had little chance to close.
The 'lethal trifecta' framing
ESET describes the underlying exposure through three conditions that, together in one agent, create risk: the agent can reach sensitive data, it processes content originating from outside the company, and it can communicate or act on external systems. A single workflow — an agent pulling files from a shared drive, parsing inbound email, and firing off messages on its own — checks all three boxes simultaneously. Removing any one leg, the firm notes, reduces the risk substantially. ESET has also documented more than 100 distinct tools built specifically to disable endpoint detection and response (EDR) software, most abusing vulnerable drivers, with new variants appearing on a regular basis — a sign that attackers are investing in disabling defenses, not just bypassing them.
What budget-holders should ask their team
For SMBs with lean IT staff, the practical questions are about visibility and ownership rather than tooling alone. Leaders should ask: which AI agents and skills are currently connected to company systems, and who approved each one? Does any single agent combine data access, external content exposure, and outbound communication in one workflow? Is there a documented AI usage policy, or is one only likely to appear after an incident? And for phishing and patching — given the gap between AI-assisted and standard phishing click rates, and the share of vulnerabilities exploited at or before disclosure — does the current detection and response arrangement include monitoring of what agents pull in and act on, not just what employees click?
Produced by the WebPulse Newsroom with AI assistance from the original reporting credited below, and checked against that source by our editorial review. How we use AI.
Original reporting: ESET.