- REA, an open-source GitHub project, lets AI agents study apps without source code. 404 Media counted more than 342,000 stars on it.
- Shipped code has long been readable with enough skill. AI agents lower the effort, so protection by obscurity weakens.
- Ask engineering what ships inside your apps, which products rely on obscurity, and who approved any use of such tools.
Shipping software means shipping a copy
When a company sells an app, it hands customers a working copy of its code. For years, the main protection was effort. Turning that code back into something a person can read took skill, time and costly tools.
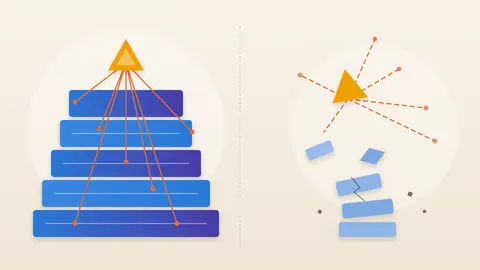
A viral open-source project signals how much attention this shift is getting. The lesson here is that closed software was protected by the cost of studying it, not by secrecy. AI agents are built to lower that cost.
What happened
The project is called Reverse Engineer Anything, or REA, and is published on GitHub by morluto. Its README describes a simple workflow. You point an AI agent at an app and ask how one feature works. The agent does not need the app's source code. It returns an explanation with its evidence and can help you build your own version.
404 Media reported on October 20 that REA had passed 342,000 GitHub stars at the time of writing, and called it viral. Stars are GitHub's bookmarks, a rough measure of attention rather than of real use.
The same article describes a wider wave of AI-driven device hacking over the same weekend. People swapped the software on smart TVs, turned smart picture frames into calendars, stripped ads from baby monitors and revived bricked Lululemon mirrors. The article does not say REA was used for these projects.
The one named example did not use REA. A user called Gathin posted on X that Claude Code located his parents' TV on the home network, deleted 25 Xiaomi packages and wrote a replacement launcher. 404 Media says the post allegedly reached more than 6 million views.
How it works
REA connects an AI agent to analysis tools through MCP, a standard way for an agent to call outside software. According to the README, those tools can examine compiled desktop programs, JavaScript and Electron apps, .NET assemblies (compiled .NET code) and websites.
For native programs, REA leans on a disassembler the user already has, such as Hopper, Ghidra or IDA. These tools turn compiled machine code back into readable assembly and rough pseudocode. JavaScript analysis needs no such engine. REA reads the files directly and recovers the modules and how they connect.
The agent then follows the relevant code, asks follow-up questions, and can write and test its own version. The README says the analysis runs on the user's machine. It adds that the agent receives the results, and the agent's model provider has its own data policy.
The project's showcases show the method at small scale. In one, REA helped rebuild a sound-panning routine from the game DX-Ball. The README reports that the rebuilt routine matched the original on 3,205 x86 test cases and reproduced all 63 bytes of the compiled function. Another showcase traces how Notion's Electron app passes clipboard data from its interface to its main process.
These are worked examples. They do not show that a large commercial product can be cloned end to end, and the README does not claim that.
Who carries the risk
Software makers face the plainest exposure. Logic that ships inside an app or web page can be studied by anyone who holds the file. That has long been true. What changes is how many people can now try.
Mike Nolan studies the politics of open source software. He told 404 Media that the software engineers he hears from say software-as-a-service is dying as a business model. In his words, recreating the functionality you want is "becoming so easy" with AI. He also doubted that many companies would adopt clones. Maintaining software is hard work, he said, and clones may not be reliable enough.
Buyers and device owners sit on the other side. AI agents of this kind are being used to restore features a vendor removed or abandoned. 404 Media describes that happening with TVs, baby monitors and mirrors. It names Claude Code in the TV case and does not name the tools behind the others.
On legality, the README says REA is meant for lawful work on software the user owns or is authorized to examine. 404 Media describes the wider trend as a mix of hacking, cloning and what it calls stealing. Whether a given use is lawful is a question for counsel, not for the tool.
Questions to put to your team
First, ask engineering what logic and what credentials ship inside your apps and web bundles. Assume a determined reader can see them, and move sensitive logic to servers you control.
Second, ask which of your products rely on obscurity as their only protection. Licensing, contracts and service quality are sturdier ground.
Third, check your vendors. If a device or app you depend on lost support, what would you do? The 404 Media article describes owners already reviving abandoned devices with AI tools.
Fourth, if staff use tools like REA, ask who approved it. The README requires that commercial tools such as IDA Pro and Hopper be legally obtained and licensed.
A shipped app was never a vault. It was a locked door that took skill to pick, and AI agents are making that skill cheaper.
Produced by the WebPulse Newsroom with AI assistance from the original reporting credited below, and checked against that source by our editorial review. How we use AI.
Original reporting: morluto (Reverse Engineer Anything project, github.com/morluto/rea).