- A GitHub advisory says a text field in PraisonAI's agents.yaml file can become Python code that runs when an operator deploys the project.
- The risk sits on the deploy machine, which may hold model, API and deployment credentials. The attacker needs the operator to deploy a malicious project file.
- Review project config files like code, deploy from clean environments, and ask engineers whether your version encodes generated values safely.
A setting should be data, not an instruction
A configuration file should hold settings, such as a name, a port or a path. It should not hold instructions. A tool that turns settings into program code can blur that line without anyone noticing.
A GitHub advisory published on October 8, 2026 describes this in PraisonAI. Its projects are defined in a file called agents.yaml. The advisory says a text value in that file can become Python code. The code runs when an operator deploys the project.
How the flaw works
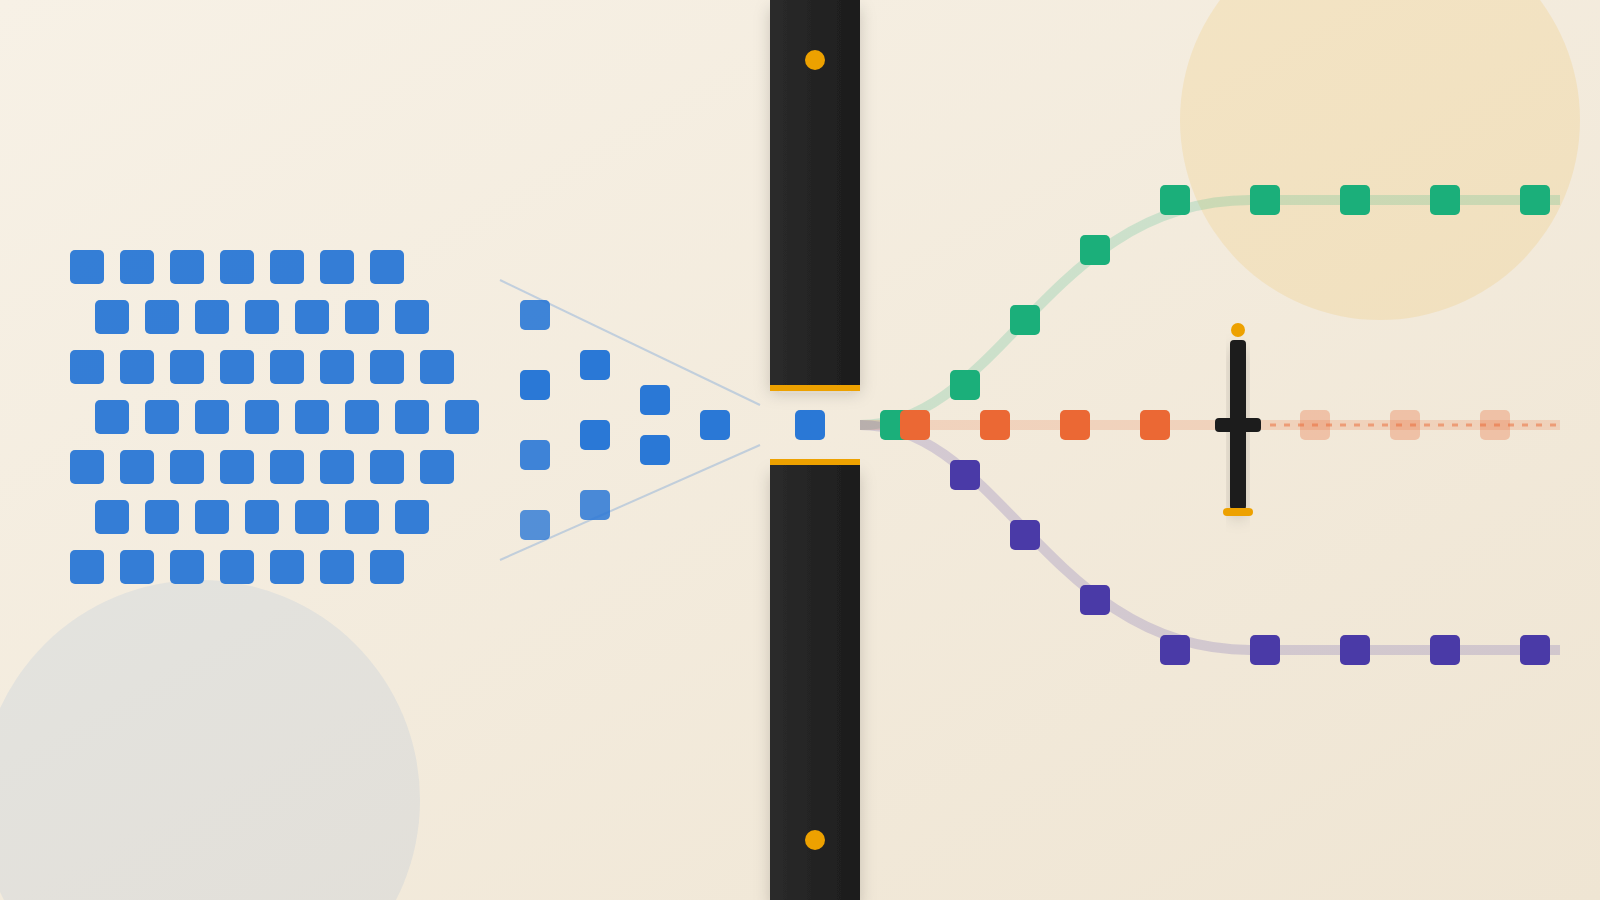
The deploy flow has four steps. First, Deploy.from_yaml() reads the project's agents.yaml. Next, a check function called validate_agents_yaml() looks at the host field. It treats that field as plain text and lets it through.
The third step hands the project to a code generator, generate_api_server_code(). It writes a Python file for a Flask web server. Flask is a common Python toolkit for web servers. In the last step, the tool launches that new file with python.
The problem is in the writing step. The generator places the host value between single quotes in the new file. It does not encode the value safely first. A value with a quote mark in it can close the string early and add its own Python expression.
That expression runs at startup, before the server handles any request. The advisory names a second field, agents_file. The generator places it into two route-handler expressions. A crafted file path can run code when those handlers are evaluated.
The pattern is old. SQL injection works the same way. Text meant as data is pasted into something that later gets executed. Here the target is Python source instead of a database query.
Who carries the risk
The advisory is clear about the limits. This is not an unauthenticated remote endpoint. The attacker needs the operator to deploy a malicious project configuration.
Authentication settings do not change the outcome. The code runs before any request arrives.
The cost falls on whoever runs the deploy command. Code that runs in the deploy process can reach whatever that process can reach. The advisory lists the operator's environment, source tree and local files. It also lists model and API credentials, and deployment credentials.
So the exposure is simple. One config file the operator did not write, run on a machine that holds production keys.
The advisory calls this a project-configuration supply-chain issue. A file that looks like harmless settings gets the trust of a reviewed script. YAML is easy to wave through in review because it looks like settings, not code.
Two cautions on scope. The proof of concept in the advisory is local-only. It stubs Flask and PraisonAI, starts no listener and calls no model provider.
Also, the advisory names a confirmed head commit, not a fixed release. Check with your engineers which version you run.
One generator, a different kind of problem
The advisory separates this report from two earlier ones about the same generated API server. GHSA-8444-4fhq-fxpq covers a Flask server created with authentication off by default. GHSA-6rmh-7xcm-cpxj, tracked as CVE-2026-44338, covers a legacy authentication issue in a generated API server.
Those two concern who may call the server. This one concerns what the generator writes before the server exists. A review of sign-in rules would not catch it.
What to ask your team
First, ask whether anyone deploys PraisonAI projects, and where those projects come from. A config file from a colleague, a contractor or a public repository needs the same review as code.
Second, ask what the deploy machine can reach. If the answer includes production keys, move deploys to a clean environment. Give it only the credentials that job needs.
Third, ask your engineers to check for the fix. The advisory advises encoding every generated Python value with repr() or json.dumps(). It also allows passing values through a JSON file, an environment variable or a command-line argument. It asks for tests with quotes, newlines and expression-splice strings. Ask whether your version has that change.
Finally, look past this one tool. Any internal system that builds scripts, Dockerfiles or pipeline files from configuration faces the same question. Do values stay data on the way in?
A setting is only a setting until something writes it into code.
Produced by the WebPulse Newsroom with AI assistance from the original reporting credited below, and checked against that source by our editorial review. How we use AI.
Original reporting: GitHub Advisory Database.