- Endor Labs found a critical flaw, GHSA-864f-rcv7-6rh4, in the code isolated-vm uses to copy data across its sandbox boundary. The isolation itself held.
- It matters because AI agents and automation tools often run code nobody reviewed, so the sandbox may be the only check.
- Confirm that isolated-vm, wherever it appears in your software, is on version 7.0.1 or 6.2.0, and audit what you pass into each sandbox.
Any company that runs code it did not write is betting on a wall. AI agents run model-generated code. Automation tools run scripts that customers paste into a form. Research from Endor Labs, a software supply chain security vendor, shows a wall can be sound and the bet can still be lost. The lesson is that a sandbox is only as strong as what you hand across it.
Why the old approach kept breaking
For years, vm2 was the usual Node.js tool for running JavaScript you do not trust. Endor Labs counts more than twenty documented escapes from it before it was deprecated.
The researchers trace this to a design choice. Guest code and host code lived in one V8 context. V8 is the JavaScript engine inside Chrome and Node.js. Both sides shared two things: the heap and the built-ins.
The heap is the memory where objects live. If two pieces of code share it, one can hold a reference to the other's objects and follow it to everything connected. The built-ins are the objects the engine supplies before your code runs, such as Object, Array and Function. They are global and can be changed.
That makes two attacks possible. Untrusted code can rewrite a built-in's behaviour, so the host runs attacker code when it uses that built-in. Or it can reach the host's Function constructor, which turns text into live code with the host's privileges. Endor Labs says vm2 tried to stop this with proxies and careful wrapping. It describes each escape as a variation on one theme: the separation was laid on top of a shared engine instead of being built into it.
What an Isolate changes
V8's answer is the Isolate. Each one is a separate engine instance with its own heap, its own garbage collector and its own copy of the built-ins.
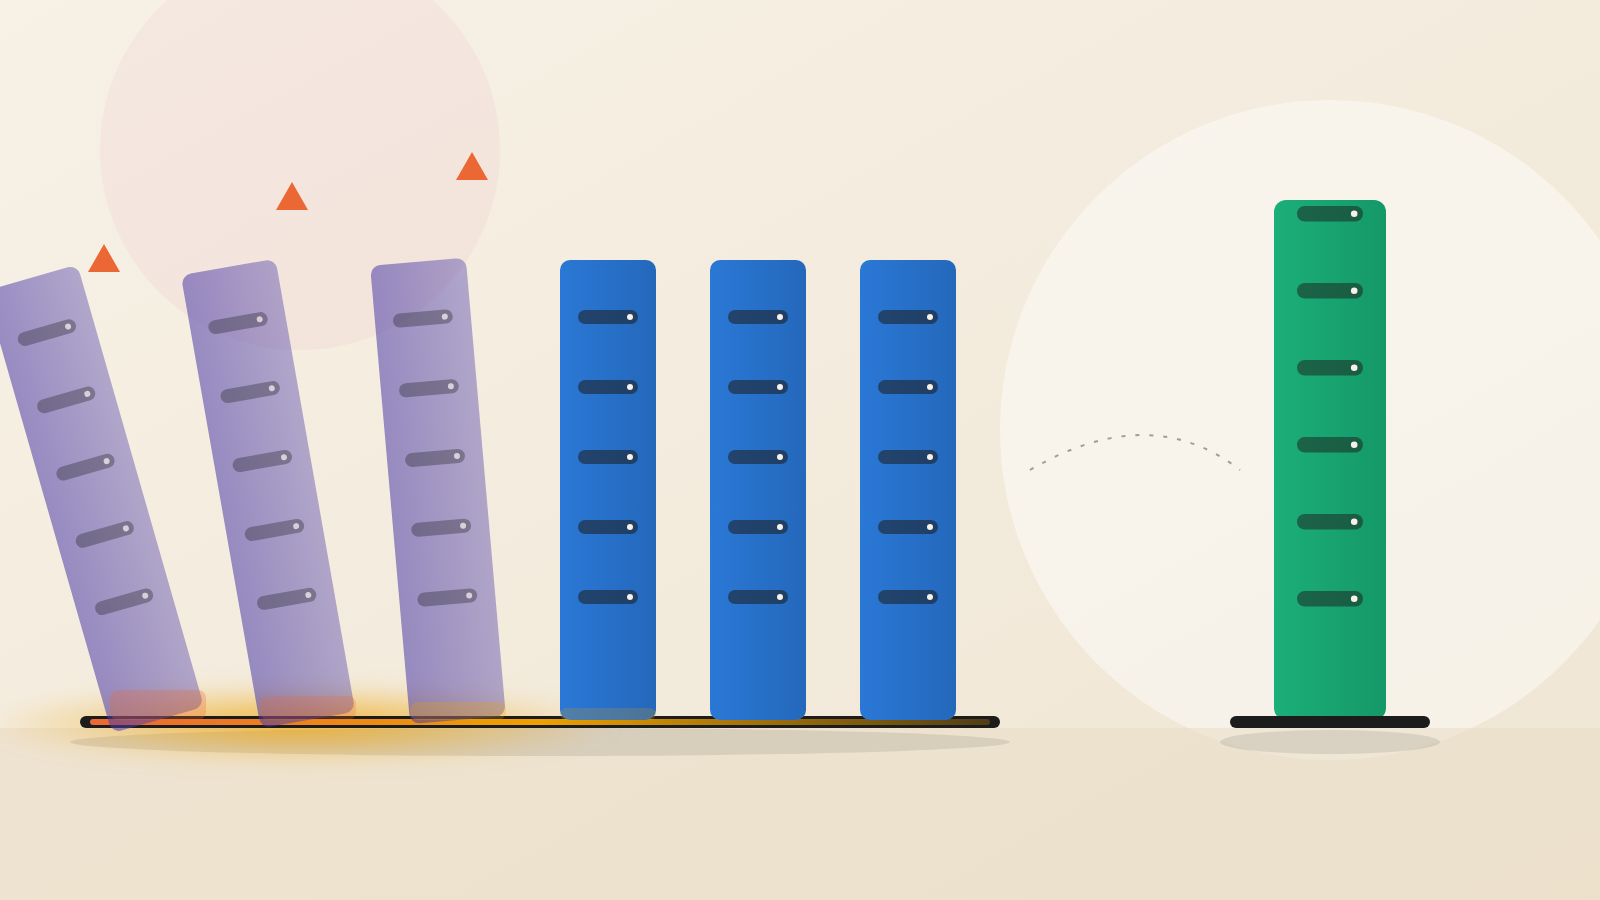
Separate heaps mean no pointer leads from guest objects to host objects. Walking the object graph to find something useful stops working, because the graph ends. Separate built-ins mean the guest can rewrite its own Array and Function and the host is unaffected.
In Node.js, the package that provides this is isolated-vm. Endor Labs says it draws over a million downloads a week. It names Rocket.Chat, Directus, Budibase, Mastra and n8n as projects that use or recommend it for user-written or model-generated scripts.
Where the wall was tested
Isolated code that cannot communicate is useless, so data must cross. Because nothing is shared, values are copied: packed up on one side and rebuilt on the other. isolated-vm also offers Reference, a handle the host deliberately passes in.
That copying is done by C++ code holding raw pointers into both heaps at once. The flaw, tracked as GHSA-864f-rcv7-6rh4, was disclosed by Endor Labs in August 2026 and rated critical. It sits in that copying code. Guest code could make the host's own C++ follow a value the guest controlled. The researchers describe a path that began as a crash the guest could trigger on purpose and grew into the ability to redirect what the host runs.
The Isolate itself held. Endor Labs says V8's memory isolation was not defeated. The weakness was in the binding code around it. The maintainer fixed the flaw in versions 7.0.1 and 6.2.0.
The idea to take from this
Think of a vault with a very good wall and a mail slot. Attention goes to the wall. The slot is where the traffic is. A sandbox works the same way. Endor Labs' point is that the true perimeter includes whatever you expose to the guest, not only the isolation itself. In this case, a single Reference was enough to reach the vulnerable code.
This matters more as code from AI models becomes routine input. That code may not get the review a pull request gets. In many setups, the sandbox is the main check.
One caveat: this is one disclosed flaw in one package, reported by a vendor that sells security tooling. The source does not report exploitation. It also does not show that Isolates are weaker than older approaches. It shows that the code around them needs scrutiny too.
Questions to put to your team
First, where do we run code we did not write? Include AI agents, automation steps and customer scripts. Second, which isolation does each use? Third, does any product we build or run depend on isolated-vm, directly or indirectly, and is each copy on a fixed release, 7.0.1 or 6.2.0? Fourth, what do we pass across the boundary, and does each Reference have a reason to exist? Fifth, who reviews the native code that copies data in and out?
A strong wall is a good start. The review belongs at the slot.
Produced by the WebPulse Newsroom with AI assistance from the original reporting credited below, and checked against that source by our editorial review. How we use AI.
Original reporting: Endor Labs.